The Browser-Sandbox Tunnel: Sharing Localhost Without a CLI
IT
Quick answer
Tabserve vs ngrok: Browser-Only Localhost Tunnels via WASM: quick comparison answer
Choose the tunnel tool based on the network model: public HTTPS URLs for webhooks and demos, private mesh access for internal apps, and managed infrastructure when policy controls matter most.
Which tunnel tool is best for public webhook testing?
Use a public HTTPS localhost tunnel with stable URLs. InstaTunnel focuses on webhook testing, demos, OAuth callbacks, and MCP endpoint workflows.
When should I choose a private network tool instead?
Choose a private mesh or Zero Trust tool when every user and service should stay inside a controlled private network.
Modern development teams are increasingly distributed, yet enterprise security teams are locking down corporate networks tighter than ever. If you work inside a strict IT environment, you know the struggle: Endpoint Detection and Response (EDR) agents block unauthorized executable binaries, and firewall configurations terminate outbound SSH connections. In these zero-trust environments, traditional developer tools fail.
When you need to share a locally running web app with a remote stakeholder, test a webhook from an external service, or debug an API from a locked-down corporate Chromebook, downloading a tunneling daemon simply isn’t an option. Enter the “browser-only tunnel” — and specifically, the tool that put this pattern on the map: Tabserve.
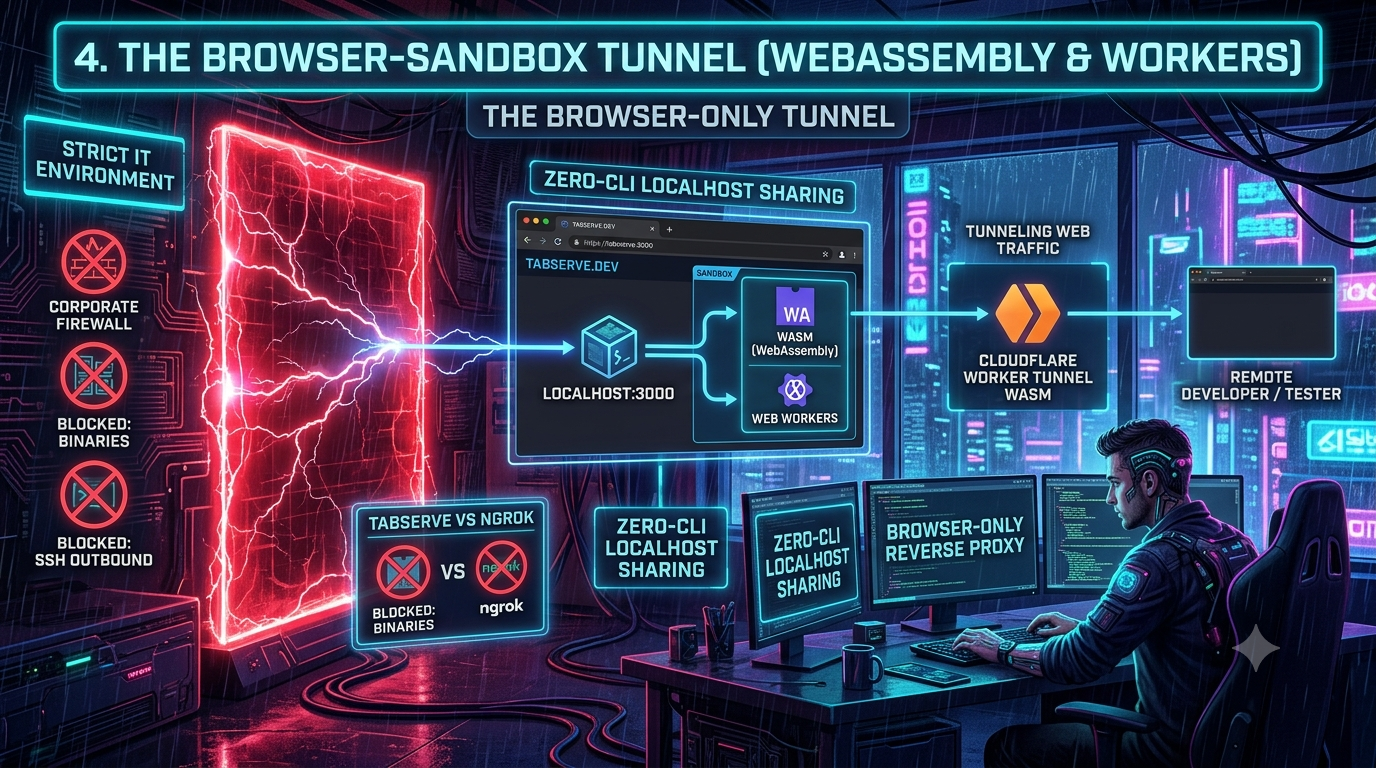
By leaning on WebSockets and browser Web Workers, this class of tool runs the tunneling process natively inside the browser sandbox. Because it operates entirely within a standard tab over a standard HTTPS port, it sidesteps a lot of the network restrictions that block CLI-based tools. This piece walks through how the architecture actually works, corrects a common misconception about it, and gives an honest, current comparison against ngrok — including a live problem with Tabserve’s own domain that changes the practical advice here.
1. The Enterprise Network Dilemma
Historically, exposing a local dev server (http://localhost:3000) required a reverse proxy: a lightweight agent on your machine that opens a persistent, secure outbound tunnel to a public server. Tools like ngrok, Localtonet, or Cloudflare’s cloudflared daemon do this well, but they share a requirement: you install a binary or use a CLI. In strict IT environments, that creates friction:
- Binary execution blocks. Application whitelisting policies mean an unsigned executable can’t run.
- No admin privileges. Installing a system-level service or modifying
PATHneeds admin rights that developers on VDI or locked-down hardware don’t have. - Protocol filtering. Corporate firewalls commonly filter port 22 outright, and shifting SSH to a non-standard port (2222 is the typical convention, not a fixed universal alternate) doesn’t reliably help once deep packet inspection is in play.
If you can’t run an executable and can’t rely on SSH, you’re stuck on localhost — but IT almost always has to allow a browser and outbound HTTPS on port 443. That’s the gap a browser-sandbox tunnel exploits.
2. Anatomy of a Browser-Only Reverse Proxy
A browser-only reverse proxy moves the routing logic from a system-level daemon into the browser tab itself. Instead of downloading anything, you open a web page.
The flow, without any installed software:
- The public edge. The tunneling service runs a public edge server — in Tabserve’s case, a single Cloudflare Worker. When a remote user hits your tunnel URL, the Worker catches the request.
- The WebSocket connection. The open browser tab holds a persistent WebSocket connection to that Worker. To a corporate firewall, this is indistinguishable from any other live web app — a chat client, a dashboard, a collaborative doc.
- Request marshalling. The Worker serializes the incoming HTTP request (method, headers, body) and pushes it down the WebSocket to the tab.
- Local execution. A Web Worker running in that tab deserializes the payload and issues the request against your local server (e.g.,
http://127.0.0.1:8080) using the browser’s nativefetch(). - Response proxying. The local server’s response is serialized and sent back up the WebSocket to the Cloudflare Worker, which returns it to the remote user.
The entire loop happens inside the browser sandbox: no CLI, no elevated permissions, no install.
3. What’s Actually Under the Hood: Cloudflare Workers + Web Workers (Not WASM)
Here’s a correction worth making up front, because it’s easy to find versions of this story — including earlier drafts of this piece — that describe Tabserve as a WebAssembly (WASM) project. It isn’t. Tabserve’s own repositories describe it plainly: “Tabserve is a web app that uses browser web workers as a reverse proxy.” The Worker component is a Cloudflare Worker written in ordinary JavaScript/TypeScript, and the local proxying happens via Web Workers running standard JS in the browser tab — not compiled WebAssembly modules.
That distinction matters for two reasons:
- WASM and Web Workers solve different problems. A Web Worker moves work off the main thread so the page’s UI doesn’t freeze while requests are marshalled — that’s exactly what Tabserve needs, and it’s what it uses. WebAssembly is about running near-native-speed compiled code in the browser; real production uses of it in proxying exist (the Proxy-Wasm ABI used by Envoy and similar edge proxies is a legitimate, separate example), but it isn’t what powers this particular tool.
- Durable Objects are the actual state layer. The Cloudflare Worker side uses Durable Objects with the WebSocket Hibernation API to hold each tunnel’s connection open cheaply — the object “sleeps” between messages so you’re only billed for active traffic. Notably, Durable Objects required Cloudflare’s $5/month Workers Paid plan when Tabserve was first built (a 2023 GitHub issue on the project shows a deploy failing for exactly that reason). Cloudflare moved Durable Objects onto the Workers Free plan in April 2025, with free-plan usage limits still applying — so self-hosting the Tabserve Worker no longer strictly requires a paid Cloudflare account, though heavier use will still hit free-tier ceilings.
Tabserve’s own documentation is also upfront about real constraints worth knowing before you rely on it:
- HTTP(S) only. No TCP or UDP — this is a hard limit of routing everything through the browser’s
fetch()API, not a missing feature. - Throughput ceiling. Roughly 100–500 requests per second.
- A 5 MB response can stall things. Large responses block the Worker/Web Worker event loop and slow down all traffic on that domain until it clears.
- The tab has to stay open and awake. Some browsers try to suspend inactive Web Worker threads; the project notes Chrome and Firefox desktop hold up fine over multiple days, but this hasn’t been heavily tested across every browser and OS combination.
4. A Live Complication: tabserve.dev No Longer Points to Tabserve
This is the kind of thing a “current state” check exists to catch, and it changes the practical advice for this piece. As of this writing, tabserve.dev — the project’s own domain — no longer hosts Tabserve. It currently resolves to an unrelated Indonesian online-gambling/T-shirt storefront page, with no trace of the original tool. The GitHub organization (emadda/tabserve, the issue tracker, and emadda/worker-tabserve-reverse-proxy, the actual Worker source) is still up and still references tabserve.dev as the canonical site in its README, but the domain itself has evidently lapsed and been picked up by an unrelated party.
Practically, this means:
- Don’t type
tabserve.devinto a browser expecting the tool. It’s not malicious, as far as could be determined, just squatted — but it’s also not Tabserve. - The only current path to using it is self-hosting. Both repos are open source (the Worker under
emadda/worker-tabserve-reverse-proxy, the web UI underemadda/tabserve). You deploy the Worker to your own Cloudflare account and domain viawrangler, wire a Workers Route (*.your-domain.com/*), paste your ownAUTH_TOKENinto the web UI’s config, and only then do you get the “visit a page, get an HTTPS URL” experience the concept promises. - This softens the “zero-CLI” pitch somewhat. The end user hitting your tunnel URL and you, tunneling traffic day-to-day never touch a CLI. But standing the thing up in the first place — deploying a Worker, configuring DNS, setting an auth token — is a one-time
wranglerand Cloudflare dashboard exercise, typically done once by whoever sets it up for a team, not a CLI-free experience end to end.
This is worth internalizing as a general lesson about this whole category of tool: a browser-sandbox tunnel’s biggest advantage (no installed binary to go stale) comes with a different fragility (a single domain that can lapse, get squatted, or otherwise vanish, taking the “product” down with it even though the code is fine).
5. Tabserve vs. ngrok: An Honest Comparison
| Capability | ngrok | Tabserve (self-hosted) |
|---|---|---|
| Execution environment | System-level binary/daemon | Browser tab (Web Workers) + your own Cloudflare Worker |
| Setup | Download CLI, ngrok config add-authtoken, run | One-time: deploy Worker to your Cloudflare account, set DNS route, paste auth token into the web UI |
| Day-to-day use | Run a CLI command per tunnel | Open the (self-hosted) web page, no CLI |
| Admin privileges | Not required for basic use; may be needed for install location | Never required on the developer’s machine |
| Firewall posture | Outbound to ngrok’s edge; usually fine over 443, but a recognizable, sometimes-blocklisted binary/process | Looks like ordinary WSS traffic over 443 from inside a browser tab |
| Protocols | HTTP, HTTPS, TCP, TLS (no native UDP) | HTTP/HTTPS only — bounded by the browser fetch() API |
| Throughput | Practically limited by your plan’s bandwidth, not the protocol | ~100–500 RPS per Tabserve’s own docs; large (5 MB+) responses can stall the event loop |
| Domain/URL stability | Free tier now gets a persistent *.ngrok-free.app dev domain (no longer rotates on restart, since ngrok’s Jan 2026 pricing update); custom domains from the Hobbyist tier up | Whatever subdomain you configure on your own domain — fully in your control, but it’s your Cloudflare zone to maintain |
| Pricing (2026) | Free (3 endpoints, 1 GB/mo, 20,000 HTTP requests/mo); Hobbyist ~$8–10/mo; Pay-as-you-go from $20/mo base + usage | Free to self-host on Cloudflare’s Workers Free plan (Durable Objects now included since April 2025); usage-based limits still apply at scale |
| Target audience | Unrestricted workstations, CI/CD, production-grade needs | Locked-down corporate laptops/Chromebooks, quick one-off sharing, teams willing to self-host once |
When to use ngrok
ngrok remains the right call for unrestricted environments and anything beyond plain HTTP: raw TCP tunnels (exposing a local database directly), custom TLS certificates, or long-lived endpoints that need to survive machine reboots without you re-deploying anything. A browser-only proxy structurally cannot tunnel raw TCP, because the browser’s fetch() API has no socket-level access.
When a browser-sandbox tunnel still makes sense
If your team has (or is willing to stand up) its own Cloudflare-hosted domain, self-hosting Tabserve gives locked-down machines an HTTPS tunnel with literally nothing to install on the developer’s end — genuinely useful for a Chromebook, a VDI session that resets nightly, or a contractor’s machine you don’t control. Just budget for the one-time setup, and don’t expect a public, always-available hosted version at tabserve.dev — that door is currently closed.
6. The Future of Zero-CLI Localhost Sharing
The push toward zero-CLI localhost sharing isn’t just a workaround for strict IT; it’s part of a broader shift toward doing real development work from a browser tab. GitHub Codespaces remains a mainstream example of this for full dev environments. One correction worth making to an earlier draft’s framing: Gitpod, often cited alongside Codespaces, isn’t the same product it used to be. Gitpod Classic’s pay-as-you-go tier sunset on October 15, 2025, and the company rebranded around Ona, positioned as “mission control for software projects and software engineering agents” rather than a straightforward cloud IDE — existing users were pointed to Ona’s free tier or enterprise sales rather than a continued Gitpod Classic product.
That doesn’t undercut the underlying trend — cloud-based dev environments accessed entirely through a browser are still very much a going concern — it just means Gitpod specifically is no longer a clean like-for-like example in 2026.
Webhook testing remains one of the clearest use cases for any ephemeral browser tunnel: catch a Stripe or GitHub webhook, verify your handler, close the tab, done — the tab’s lifecycle doubles as an automatic security boundary.
VDI environments (Citrix Workspaces and similar, common in banking, healthcare, and defense) are the other strong fit: machines that reset daily wipe any installed CLI tool along with it, so anything that needs zero persistent local install has an obvious advantage there.
Changelog
- WASM claim removed and corrected. The original draft framed Tabserve as a “Cloudflare Worker tunnel WASM” architecture. Tabserve’s own repos describe it as using browser Web Workers, not WebAssembly; rewrote Section 3 accordingly and kept WASM/Proxy-Wasm mentioned only as a separate, real-but-unrelated pattern (used in tools like Envoy), not something this tool uses.
- Added the Cloudflare Worker’s actual state mechanism (Durable Objects + WebSocket Hibernation API) and corrected its cost history: Durable Objects required the $5/month Workers Paid plan as recently as a 2023 issue on the project, but moved to the Workers Free plan in April 2025 (with free-tier usage limits still applying).
- Added Tabserve’s own documented limitations (HTTP-only, ~100–500 RPS, 5 MB response stalls, tab-must-stay-awake caveat) — absent from the original draft, and directly relevant to whether this fits a given workload.
- Major correction: tabserve.dev is currently squatted. The domain no longer hosts Tabserve — it resolves to an unrelated storefront/gambling page. This wasn’t in scope of the original draft (which implied you could just “visit tabserve.dev”) and materially changes the advice: the tool is only currently usable by self-hosting from source. Added a dedicated section and adjusted every downstream reference to “visiting the site” to reflect self-hosting instead.
- Softened the “zero-CLI” framing to distinguish setup (which does involve
wrangler/Cloudflare dashboard work, one time) from day-to-day use (which is genuinely CLI-free). - Corrected the alternate-SSH-port claim. The original cited “port 223” as a common alternate SSH port; the actual convention is 2222 (223 doesn’t correspond to a real widely-used SSH alternate).
- Rewrote the comparison table with current 2026 ngrok pricing and features (Free: 3 endpoints/1 GB per month/20,000 requests; Hobbyist ~$8–10/month; Pay-as-you-go from $20/month base), confirmed ngrok supports HTTP/HTTPS/TCP/TLS but not native UDP, and added ngrok’s January 2026 change to persistent (non-rotating) free-tier dev domains.
- Corrected the Gitpod reference in the closing section: Gitpod Classic’s pay-as-you-go tier sunset October 15, 2025, and the product was rebranded to Ona; the original draft cited Gitpod as a current, unqualified example alongside GitHub Codespaces.
- Sources checked:
github.com/emadda/tabserve,github.com/emadda/worker-tabserve-reverse-proxy(README,wrangler.toml, Issue #1, Discussion #3), live fetch oftabserve.dev,developers.cloudflare.comDurable Objects Free plan changelog (April 2025), current ngrok pricing/feature summaries cross-referenced across independent 2026 comparison sources, andgithub.com/gitpod-io/gitpod/ Ona rebrand notice.
Related InstaTunnel pages
Continue from this article into the most relevant product guides and workflows.


Comments
Post a Comment