Modern Frontend & Mobile Testing Workflows: Tunnels, Routing, and Cache Debugging
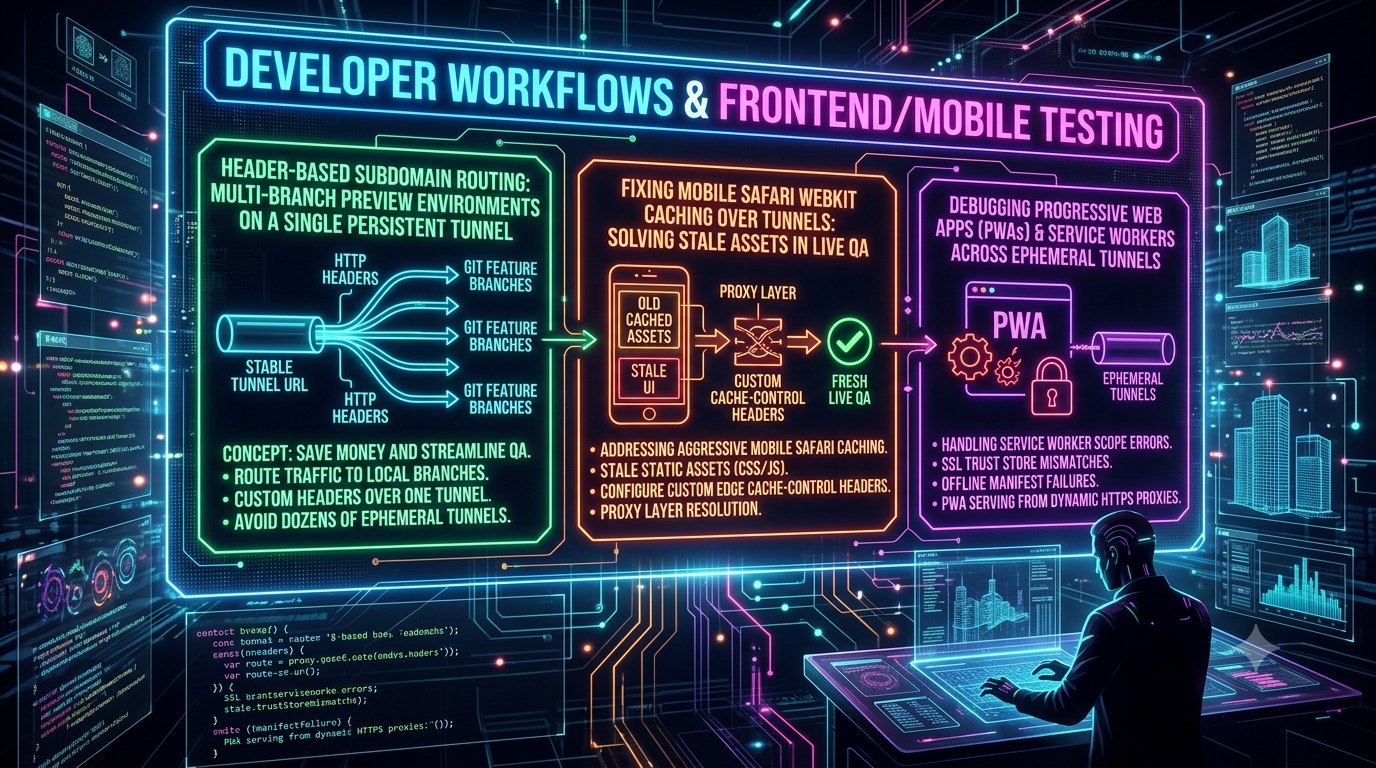
As modern engineering teams move toward continuous integration, testing local code on physical mobile devices, remote staging servers, and external webhooks has become an integral part of daily development. Localhost tunnels (such as Cloudflare Tunnel, ngrok, pinggy, and open-source reverse proxies) bridge the gap between local development environments and the public internet.
However, standard ephemeral tunneling creates engineering friction, unexpected infrastructure costs, aggressive caching bugs on Mobile Safari WebKit, and service worker registration failures in Progressive Web Apps (PWAs).
This comprehensive guide explores advanced architectural patterns and debugging strategies to optimize frontend and mobile testing workflows across persistent and dynamic HTTPS local proxies.
1. Header-Based Subdomain Routing: Multi-Branch Preview Environments on a Single Persistent Tunnel
The Problem: Ephemeral Tunnel Fatigue and Escalating Costs
In a typical feature-driven development workflow, developers work across multiple git branches simultaneously (e.g., feature/checkout-redesign, fix/auth-leak, feature/dark-mode).
The standard approach to local testing involves spinning up a separate tunnel process for every local branch or port:
# Branch 1: Checkout Redesign
ngrok http 3000 -> https://a1b2c3.ngrok-free.app

# Branch 2: Auth Fix
ngrok http 3001 -> https://x9y8z7.ngrok-free.app
This multi-tunnel model introduces several operational drawbacks:
- High SaaS Tunnel Costs: Commercial tunnel providers often gate persistent named subdomains behind premium tier pricing. Spawning dozens of simultaneous active sessions quickly hits subscription limits.
- Context Switching and Broken Webhooks: Third-party services (such as Stripe, GitHub, Twilio, or OAuth providers) require fixed callback URLs. Changing the tunnel domain every time a local server restarts breaks remote integration tests.
- Resource Overhead: Running multiple reverse proxy processes consumes system memory and background bandwidth.
The Solution: Layer 7 Routing over a Single Persistent Tunnel
Instead of establishing multiple tunnels for separate features, engineering teams can configure a single persistent tunnel with a fixed wildcard domain (*.dev.yourcompany.com) or a fixed static URL. Traffic targeting different local Git branches or dev servers is dynamically routed at Layer 7 using custom HTTP request headers.
                  ┌──────────────────────────────────────────────┐
                  │          Persistent HTTPS Tunnel             │
                  │        (e.g., https://dev.company.com)       │
                  └──────────────────────┬───────────────────────┘
                                         │
                                         ▼
                  ┌──────────────────────────────────────────────┐
                  │    Local Reverse Proxy / Router (Nginx/Caddy)│
                  │   Inspects incoming 'X-Branch' Header        │
                  └──────┬───────────────────────┬───────────────┘
                         │                       │
     X-Branch: checkout  │                       │ X-Branch: auth-fix
                         ▼                       ▼
           ┌──────────────────────────┐    ┌──────────────────────────┐
           │ Git Branch: feature/chk   │    │ Git Branch: fix/auth     │
           │ Local Server (Port 3000) │    │ Local Server (Port 3001) │
           └──────────────────────────┘    └──────────────────────────┘
By adding a custom header—such as X-Branch: checkout or X-Env-Target: auth-fix—a lightweight local reverse proxy (like Caddy, Nginx, or Traefik) intercepts incoming proxy traffic and forwards it to the corresponding local service port.
Practical Implementation: Nginx Routing Architecture
Below is an Nginx configuration designed to run locally alongside a persistent tunnel tool (such as cloudflared or a custom SSH tunnel).
# /etc/nginx/nginx.conf or local dev nginx.conf

http {
    # Map the custom request header 'X-Branch' to an upstream port
    map $http_x_branch $upstream_port {
        default         3000; # Default feature branch / main application
        "checkout"      3000; # Branch: feature/checkout-redesign
        "auth-fix"      3001; # Branch: fix/auth-leak
        "dark-mode"      3002; # Branch: feature/dark-mode
    }

    server {
        listen 8080;
        server_name localhost dev.company.com;

        location / {
            # Route request dynamically based on the mapped header value
            proxy_pass http://127.0.0.1:$upstream_port;

            # Pass standard proxy headers
            proxy_set_header Host $host;
            proxy_set_header X-Real-IP $remote_addr;
            proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
            proxy_set_header X-Forwarded-Proto $scheme;

            # Ensure WebSockets function across all feature environments
            proxy_http_version 1.1;
            proxy_set_header Upgrade $http_upgrade;
            proxy_set_header Connection "upgrade";
        }
    }
}
Routing Traffic via Browser Extensions & Mobile Testing
Once the single tunnel is established pointing to 127.0.0.1:8080, QA engineers and developers can seamlessly switch between branch environments on the same domain:
- Desktop Browsers: Use browser extensions like ModHeader or Header Editor to inject
X-Branch: dark-modeglobally into outgoing HTTP requests. - Mobile Devices (iOS / Android): Use proxy tools such as Charles Proxy, Proxyman, or custom test harness wrappers to set request headers automatically across test suites.
- Automated Cypress / Playwright Suites: Pass custom headers directly through test configuration suites:
// Playwright example for header-based environment targeting
import { test, expect } from '@playwright/test';

test.use({
  extraHTTPHeaders: {
    'X-Branch': 'checkout',
  },
});

test('test checkout flow on specific branch over single tunnel', async ({ page }) => {
  await page.goto('https://dev.company.com/checkout');
  // ... test implementation
});
Financial & Workflow Comparison
| Metric | Ephemeral Multi-Tunnel Setup | Single Persistent Header-Routed Tunnel |
|---|---|---|
| Active Tunnel Count | 5–15 per developer | 1 persistent tunnel |
| SaaS Licensing Cost | High (Paid plans per user/tunnel) | Low to Free (Single domain/SSH) |
| Webhook Stability | Fragile (URLs change continuously) | Fixed (Single callback URL) |
| QA Switching Time | High (Re-entry of dynamic URLs) | Low (Simple header toggle) |
2. Fixing Mobile Safari WebKit Caching Over Tunnels: Solving Stale Assets in Live QA
The Problem: WebKit’s Aggressive Disk & Memory Caching
When performing live QA testing of responsive web applications on physical iPhones or iPads using Safari, developers often run into persistent stale asset bugs. A CSS or JavaScript file updated on the local machine may fail to reflect on the connected iOS device, even after multiple page refreshes.
This behavior stems from the underlying WebKit engine in iOS Mobile Safari. To conserve battery life, network bandwidth, and CPU cycles on mobile hardware, WebKit enforces aggressive disk and memory caching policies:
- Heuristic Caching: If an incoming HTTP response lacks explicit cache directive headers (
Cache-Control), WebKit calculates an implicit expiration time based on theLast-Modifiedheader. - Conditional Validation Bypass: Under weak cellular or tunneling latency conditions, Mobile Safari may bypass revalidation (
304 Not Modified) checks entirely, serving outdated static JS/CSS directly from the local WebKit cache. - Tunnel Re-use Overhead: Tunneling proxies often append or strip specific HTTP headers during dynamic proxying, triggering WebKit's fallback caching behavior.
The Fix: Configuring Custom Edge Cache-Control Headers
To eliminate stale asset issues on iOS devices during live testing, custom HTTP response headers must be set at the reverse proxy layer (or tunnel edge). This forces WebKit to bypass local disk storage and validate every asset request with the upstream development server.
Essential Response Headers for Live QA
To prevent aggressive mobile caching, ensure your local web server or proxy returns the following response header block for static assets:
Cache-Control: no-cache, no-store, must-revalidate, max-age=0
Pragma: no-cache
Expires: 0
Implementing Cache Override Rules in Development Proxies
Option A: Caddy Server Configuration
Caddy provides a clean syntax for injecting headers across development traffic:
dev.company.com {
    reverse_proxy 127.0.0.1:3000

    # Match all static assets
    @static {
        file
        path *.js *.css *.html *.json
    }

    # Inject aggressive cache-busting headers
    header @static {
        Cache-Control "no-cache, no-store, must-revalidate, max-age=0"
        Pragma "no-cache"
        Expires "0"
    }
}
Option B: Nginx Proxy Header Override
In Nginx, ensure add_header directives override any headers coming from lower-level framework middleware:
location ~* \.(js|css|html|json)$ {
    proxy_pass http://127.0.0.1:3000;

    # Hide existing upstream cache headers to prevent duplicates
    proxy_hide_header Cache-Control;
    proxy_hide_header Pragma;
    proxy_hide_header Expires;

    # Apply strict non-caching headers for mobile QA
    add_header Cache-Control "no-cache, no-store, must-revalidate, max-age=0" always;
    add_header Pragma "no-cache" always;
    add_header Expires "0" always;
}
Advanced Debugging: iOS Web Inspector over USB
When headers alone do not clear an existing stuck cache state on an iOS device, inspect the Mobile Safari runtime directly:
- On the iOS Device: Navigate to Settings > Safari > Advanced and toggle Web Inspector to ON.
- Connect the iPhone to a macOS host machine using a Lightning or USB-C cable.
- Open desktop Safari on the Mac, navigate to the Develop menu, select the attached iOS device, and choose the active tunnel URL page.
- In the Web Inspector panel, navigate to the Storage or Network tab, check Disable Caches, and execute a hard reload (
Cmd + R).
3. Debugging Progressive Web Apps (PWAs) & Service Workers Across Ephemeral Tunnels
Testing Progressive Web Apps over ephemeral tunnels exposes structural edge cases in how web browsers enforce security boundaries for Service Workers, Web App Manifests, and offline caching layers.
 ┌────────────────────────────────────────────────────────────────────────┐
 │                        PWA Security Criteria                           │
 ├───────────────────────────────────┬────────────────────────────────────┤
 │ 1. Valid HTTPS Context            │ Ephemeral dynamic domain requires  │
 │                                   │ trusted SSL certificate chain.     │
 ├───────────────────────────────────┼────────────────────────────────────┤
 │ 2. Correct Service Worker Scope   │ Script location determines max     │
 │                                   │ scope (e.g., /app/sw.js -> /app/). │
 ├───────────────────────────────────┼────────────────────────────────────┤
 │ 3. Offline Cache Matching         │ Hardcoded hostnames in precache    │
 │                                   │ manifests cause fetch failures.    │
 └───────────────────────────────────┴────────────────────────────────────┘
Critical Issue 1: Service Worker Scope & Header Mismatches
By default, the location of the Service Worker file determines its maximum allowed scope. A script served from https://tunnel-domain.com/assets/sw.js can only control pages under the /assets/ path hierarchy.
If the PWA application runs at the root path (/), browser registration will throw a security exception:
SecurityError: The path of the provided scope ('/') is not allowed by the max scope
for the given script location ('/assets/sw.js').
The Fix: The Service-Worker-Allowed Header
If your development build places sw.js in a subdirectory, configure your upstream development server or tunnel proxy to return the Service-Worker-Allowed HTTP response header:
HTTP/1.1 200 OK
Content-Type: application/javascript
Service-Worker-Allowed: /
When registering the Service Worker in JavaScript, explicitly define the target root scope:
if ('serviceWorker' in navigator) {
  navigator.serviceWorker.register('/assets/sw.js', {
    scope: '/'
  })
  .then((registration) => {
    console.log('Service Worker registered successfully with scope:', registration.scope);
  })
  .catch((error) => {
    console.error('Service Worker registration failed:', error);
  });
}
Critical Issue 2: SSL/TLS Trust Store Mismatches on Dynamic HTTPS Proxies
Service Workers require a Secure Context (HTTPS or localhost). When serving local apps through self-signed TLS proxies or custom local tunnels, physical mobile devices often block Service Worker installation due to missing certificate trust chains.
- Android Chrome Error:
DOMException: Failed to register a ServiceWorker... An SSL certificate error occurred when fetching the script. - iOS Safari Error:
Fetch API cannot load... due to access control checks.
Resolution Strategy
- Use Trusted CA Tunnels: Ensure your tunnel solution automatically provisions valid, publicly trusted Let's Encrypt or zero-trust certificates (e.g., Cloudflare Tunnel, Pinggy, or official custom domains) rather than untrusted local self-signed certificates.
- Installing Root CAs on Test Hardware: If using local self-signed certificates (such as
mkcertormkcert-tunnel), install the local CA root certificate directly onto the test device trust store: * iOS: Profile Installation -> Settings > General > About > Certificate Trust Settings -> Enable Full Trust for Root Certificates. * Android: Settings > Security > Encryption & Credentials > Install a Certificate > CA Certificate.
Critical Issue 3: Stale Precache Manifests & Ephemeral Domain Mismatches
PWA build tools (such as Workbox, Vite PWA Plugin, or Next-PWA) generate static precache manifests during the local build process. These manifests map asset URLs for offline usage.
If your build pipeline bakes absolute URLs (e.g., http://localhost:3000/main.js or https://old-tunnel-123.ngrok-free.app/main.js) into the Service Worker cache manifest, loading the app over a new ephemeral tunnel domain will cause cache mismatch errors. The Service Worker will attempt to fetch assets from an inaccessible hostname, failing to install or causing infinite reload loops.
Resolution Strategy: Dynamic Relative Scoping
Ensure all precache assets are configured to use relative pathing within your build configuration:
// vite.config.js (Vite PWA Plugin Example)
import { defineConfig } from 'vite';
import { VitePWA } from 'vite-plugin-pwa';

export default defineConfig({
  plugins: [
    VitePWA({
      registerType: 'autoUpdate',
      workbox: {
        // Ensure navigateFallback and precache use root-relative paths
        navigateFallback: '/index.html',
        globPatterns: ['**/*.{js,css,html,ico,png,svg}'],
        // Exclude hardcoded host check
        modifyURLPrefix: {
          '': '/'
        }
      }
    })
  ]
});
Programmatic Unregistration for Clean Test Runs
During manual testing across changing tunnel domains, force-clear registered Service Workers and associated CacheStorage buckets programmatically using a browser utility script:
// Dev utility: Run in browser console to reset PWA state across tunnel switches
async function purgeTunnelPWA() {
  // 1. Unregister all Service Workers
  const registrations = await navigator.serviceWorker.getRegistrations();
  for (let registration of registrations) {
    await registration.unregister();
    console.log('Unregistered SW:', registration.scope);
  }

  // 2. Clear all CacheStorage instances
  const cacheNames = await caches.keys();
  for (let name of cacheNames) {
    await caches.delete(name);
    console.log('Deleted Cache:', name);
  }

  // 3. Reload page ignoring cache
  window.location.reload(true);
}
4. Key Takeaways & Architectural Checklist
To establish a resilient, fast, and cost-effective local testing workflow across engineering teams, implement the following operational standards:
- Consolidate Tunnels: Transition away from spawning per-branch ephemeral tunnels. Deploy a single persistent tunnel paired with a local reverse proxy that routes traffic based on custom HTTP request headers (e.g.,
X-Branch). - Disable WebKit Caching on Mobile Edge: Override default caching behavior on dev proxies serving iOS devices by explicitly injecting
Cache-Control: no-cache, no-store, must-revalidate. - Validate Service Worker Boundaries: Ensure
Service-Worker-Allowed: /headers are configured when serving workers from subdirectories, and stick strictly to root-relative pathing in precache manifests to prevent cross-domain fetch failures.
Originally published at https://instatunnel.my/blog/modern-frontend-mobile-testing-workflows-tunnels-routing-and-cache-debugging


Comments
Post a Comment